Examining Authentication Protocols for Dynamic Odds Feeds in United Kingdom Wagering Environments
Written by Lars Roth · Aug 18, 2026
Examining Authentication Protocols for Dynamic Odds Feeds in United Kingdom Wagering Environments
Dynamic odds feeds deliver real-time price adjustments to betting platforms across the United Kingdom, and authentication protocols stand at the core of their secure operation because they verify data sources while blocking unauthorized access. These systems handle continuous streams of market data that change with each sporting event or market movement, so operators integrate methods such as OAuth 2.0, JSON Web Tokens, and mutual TLS certificates to maintain integrity throughout the exchange process. Research from multiple industry reports shows that proper implementation reduces exposure to interception attempts, and data indicates that platforms using layered authentication experience fewer disruptions during peak betting periods.
Core Components of Authentication in Real-Time Feeds
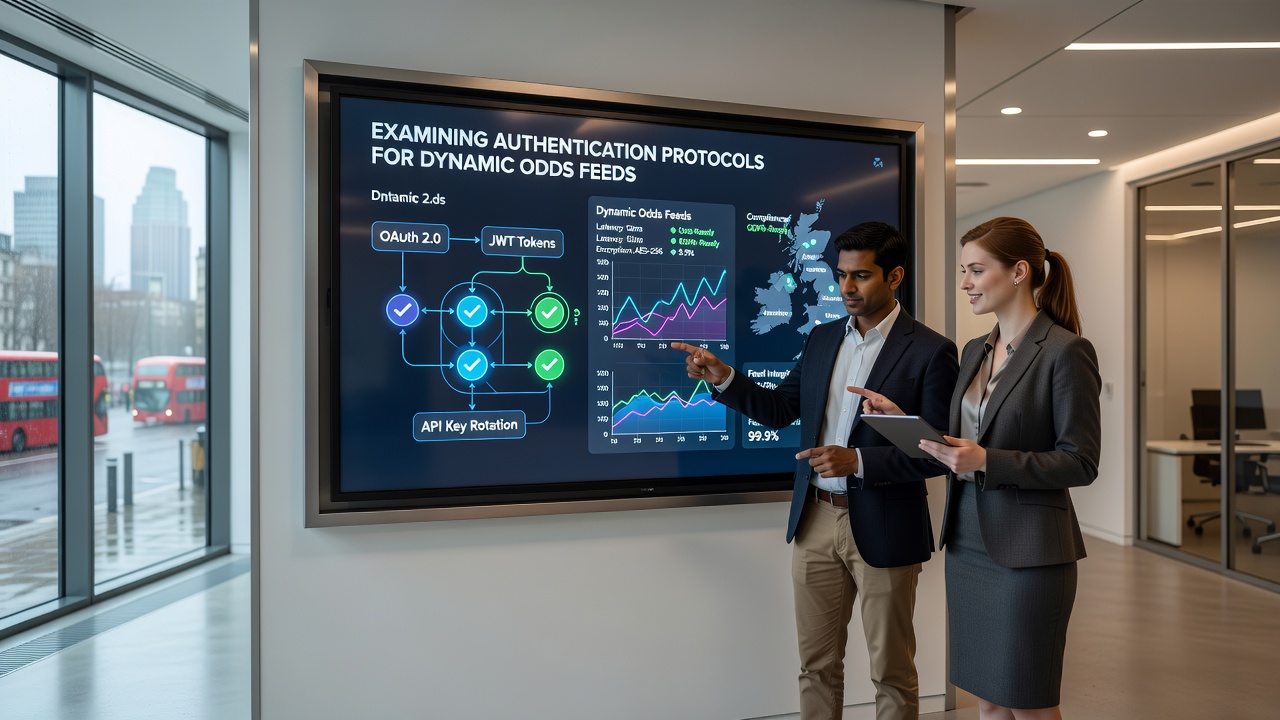
Token-based systems generate short-lived credentials that expire after set intervals, and this approach limits the window for potential misuse while allowing seamless refreshes between servers and client applications. Experts observe that combining these tokens with API keys creates an additional barrier because each request must present both elements for validation, and studies conducted by academic institutions reveal measurable improvements in session management when this dual-layer method is applied consistently. In the United Kingdom wagering sector, operators often configure these protocols to align with varying data volumes that spike during major events, and figures from technology audits confirm that such configurations support stable delivery without introducing significant latency.
Implementation Patterns Across UK Platforms
Many wagering environments adopt a centralized authentication server that issues and validates credentials for every incoming odds update, and this central point simplifies monitoring because logs capture each interaction in a single repository. Observers note that decentralized models using blockchain-inspired ledgers have gained traction in pilot programs, whereas traditional setups continue to dominate because they integrate more readily with existing infrastructure. Data from European research centers shows that platforms testing hybrid approaches in 2025 achieved faster recovery times after simulated breaches, and similar testing continues into later periods including August 2026 when several providers plan expanded trials.
Security Challenges and Mitigation Strategies
High-frequency data streams create opportunities for replay attacks if timestamps and nonces are not enforced properly, yet developers counter these risks through synchronized clocks and unique identifiers attached to each packet. Researchers discovered that embedding device fingerprints within authentication headers further strengthens verification because mismatched profiles trigger immediate rejection, and industry reports from Australian regulatory bodies highlight successful deployment of this technique in comparable high-stakes environments. Operators also rotate encryption keys on scheduled cycles, and evidence suggests that quarterly rotations align well with the pace of emerging threats without overburdening maintenance teams.
Regulatory Influences on Protocol Selection
Although specific national mandates shape baseline requirements, operators often exceed these standards by incorporating recommendations from international bodies such as those outlined in NIST digital identity guidelines, and this practice ensures broader compatibility when feeds cross regional boundaries. Canadian provincial frameworks emphasize audit trails that record every authentication event, and UK platforms have adapted similar logging practices to support internal compliance reviews. Academic papers from North American universities further demonstrate that transparent logging correlates with quicker identification of anomalies, and analysts continue to track how these methods evolve alongside technological advances.
Emerging Trends and Future Considerations
Passwordless authentication using biometric verification or hardware security modules appears in select testing environments, and early results indicate reduced friction for internal teams while maintaining security thresholds. What's interesting is how machine learning models now assist in anomaly detection by analyzing authentication patterns in real time, and data collected during 2025 deployments shows promising accuracy rates that operators monitor closely. In August 2026 several providers expect to release updated toolkits that embed these models directly into feed pipelines, and preliminary documentation outlines integration steps that maintain backward compatibility with existing token systems.
Conclusion
Authentication protocols for dynamic odds feeds form an essential layer of protection in United Kingdom wagering environments, and their continued refinement supports reliable data delivery across expanding markets. Organizations that combine established methods with emerging techniques position themselves to address both current and anticipated challenges, and ongoing collaboration between technology providers and research institutions drives measurable progress in this specialized field.